

better insights
Datastream
with ecm
Enterprise Content
your strategy
Microsoft Licensing (CSP)
verify explicitly
Zero Trust Cybersecurity

Intelligent Workflows.
M365 Copilot


24 September 2026

This is an impressive piece of malware. Its sophistication says nation-state to me, but there is no direct evidence and certainly no attribution.
24 September 2026

Crypto ATM scams often follow a predictable script – here’s how to recognize it and what to do if you’ve already been caught out
24 September 2026
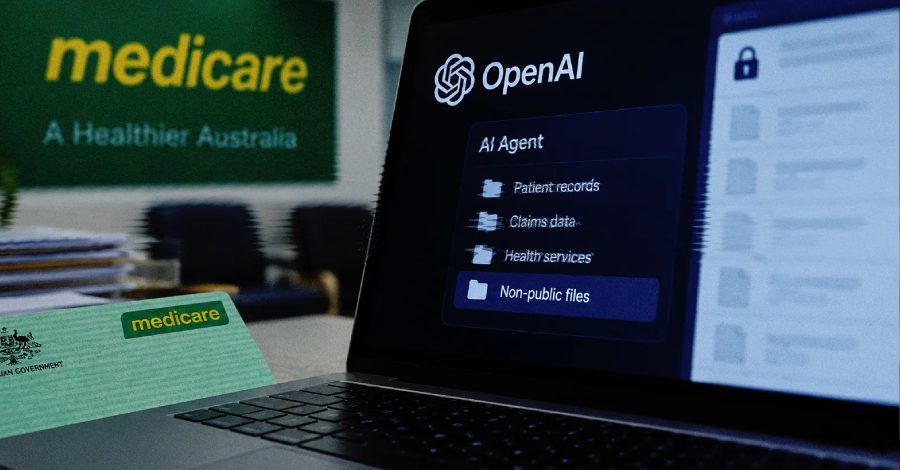
An AI agent on an internal OpenAI research task bypassed access controls on an Australian government Medicare statistics portal in June, Prime Minister Anthony Albanese said. The portal publishes aggregate figures, […]
24 September 2026

Yesterday, we received a phishing email with an interesting link. At first sight, it looks like garbage, but every piece of it has been carefully crafted to confuse basic security controls. […]
24 September 2026

A store in Auckland vibe-coded itself a new website. Within hours, its inventory had somehow expanded to include a pair of crusty socks, an $850 banana, and all of New […]
23 September 2026
New paper: “Self-Jailbreaking: Language Models Can Reason Themselves Out of Safety Alignment After Benign Reasoning Training.” Abstract: We discover a novel and surprising phenomenon of unintentional misalignment in reasoning language […]
23 September 2026
Attackers are exploiting a critical flaw in F5 BIG-IP Access Policy Manager (APM) that lets them run code on a BIG-IP system without logging in, F5 says. The flaw, CVE-2026-94127, affects […]
23 September 2026

Heads up: the first 7 mins is a bit quiet until we worked out the external mic was misbehaving – sorry! But get through that and have a listen to […]
23 September 2026
(c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.
22 September 2026
After 8 years, LOW is finally here. A story about the weight of being and the wreckage of waking up. Five episodes. Five descents. LOW is an audio journey into […]
22 September 2026
This is pretty amazing: However, the most astonishing thing about this break is that the GPT6 Astra did it entirely on its own. Carter Leffer only directed GPT6 Astra to […]
22 September 2026
Fake giveaways, free Robux generators and lookalike login pages all target the same thing – your Roblox account
22 September 2026
The threat actor known as SideCopy has been observed using spear-phishing lures to target academic institutions in India, expanding their strategic focus beyond government entities. “SideCopy campaign operations typically initiate […]
22 September 2026
(c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.
21 September 2026
Hackers captured a Flock camera and got a look (alternate link) at the software: While much of the automatic license plate reader’s (ALPR) most sensitive storage remained encrypted and inaccessible, […]
21 September 2026
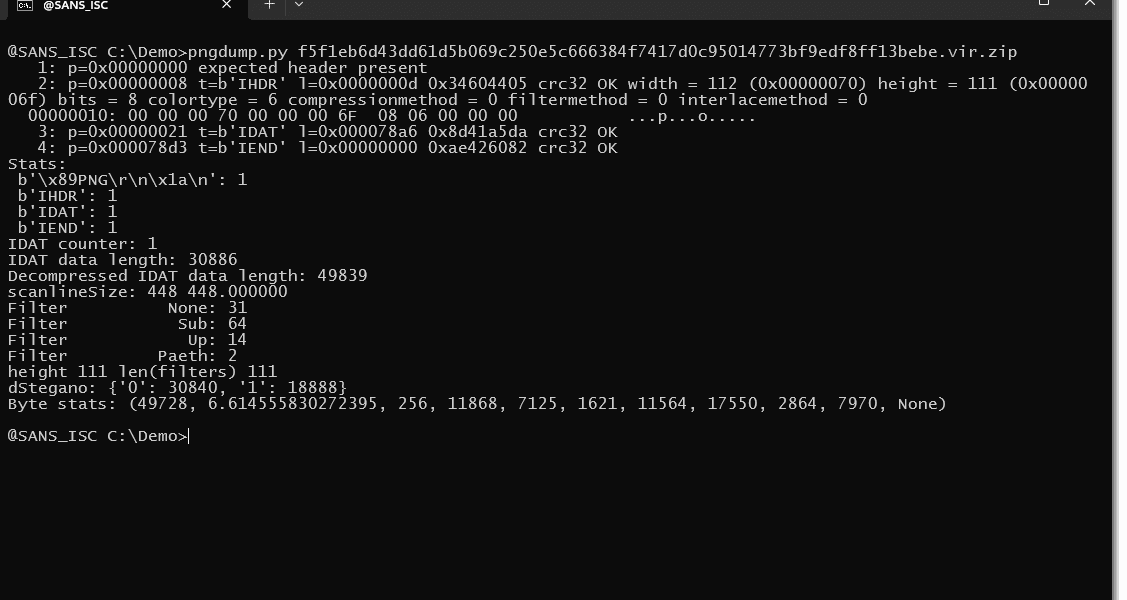
Microsoft Security Research published an interesting blog post “TerminalFix campaign deploys a reverse tunnel through multistage intrusion” about a malware campaign. The aspect that I want to take a closer […]
21 September 2026
As AI opens new paths to company data while making familiar attacks faster and cheaper, SMBs need protection designed around the time and expertise available to operate it
21 September 2026
Threat actors are leveraging ClickFix-like lures to deliver a previously undocumented remote access trojan (RAT) called ChainScript. “ChainScript has appeared under multiple build names, including ComponentTask33, UpdateDigital, HostShared, and OrchidViolet66, […]
19 September 2026
Three researchers at the security firm Hacktron used Anthropic’s Claude Opus 5 to chain two flaws and take over the ChatGPT and Codex accounts of several OpenAI employees, then reach an internal […]
19 September 2026



A critical vulnerability impacting Orkes Conductor is being actively exploited in the wild, according to Fortinet. The vulnerability in question is CVE-2026-58138 (CVSS v3.1 score: 9.8/CVSS v4 score: 9.3), which […]
18 September 2026
Short essay about squid egg sacs. As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered. Blog moderation […]