

better insights
Datastream
with ecm
Enterprise Content
your strategy
Microsoft Licensing (CSP)
verify explicitly
Zero Trust Cybersecurity

Intelligent Workflows.
M365 Copilot


6 October 2026
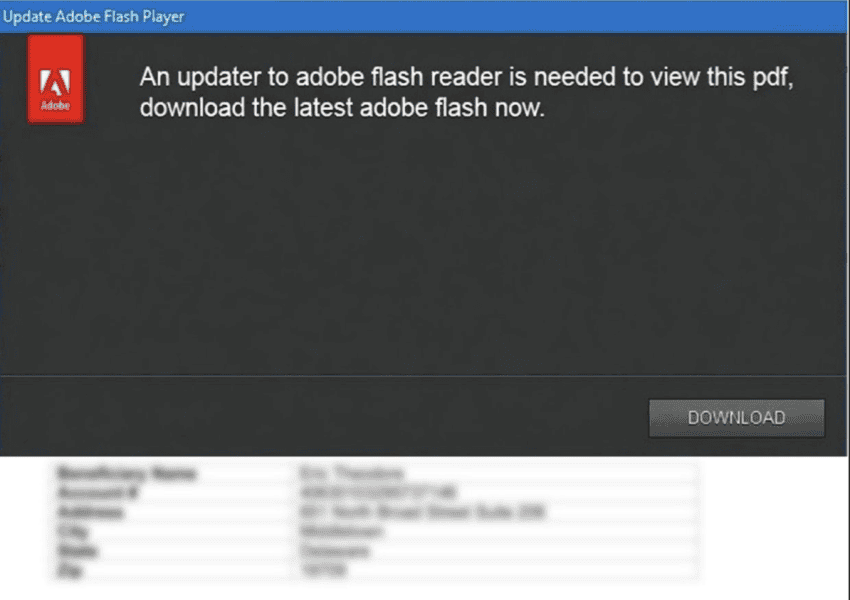
It seems that a trend started… I continue my journey discovering more RMM (“Remote Management & Monitoring”) tools abused by threat actors! A few days ago, I wrote a diary[1] about […]
6 October 2026

Google has stopped accepting product vulnerability reports through its bug bounty program for its open-source software. The change, in effect since October 1, means researchers can no longer submit security […]
6 October 2026

The word Conti struck fear in IT departments across the world. It’s a type of ransomware that you hope to never come across. Like most ransomware gangs, the Conti group […]
5 October 2026

This one is from 1809, written by Napoleon’s nephew.
5 October 2026
A critical security flaw impacting Rejetto HTTP File Server (HFS) is witnessing active exploitation attempts, according to VulnCheck. The vulnerability in question is CVE-2026-61500 (CVSS score: 9.3), a case of […]
5 October 2026

ISC Stormcast For Monday, October 5th, 2026 https://isc.sans.edu/podcastdetail/10122, (Mon, Oct 5th)
(c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.
5 October 2026

Categories: Threat Research Tags: advisory, vulnerability, Citrix
4 October 2026

I’m in Denmark! Well, just, I’m now at Copenhagen airport ready to begin the long trek home, with the final event at GOTO now done and going just perfectly. This […]
4 October 2026
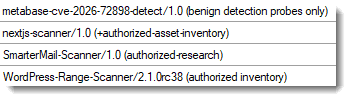
Sometimes I have to smile, or my interest is triggered, when I review new User Agent Strings in the honeypot logs. Like when I see an “authorized” scan: Or when […]
4 October 2026

A suspected member of the ShinyHunters digital extortion group, who goes by the online alias “Rey,” has been allegedly detained by authorities in Jordan, Reuters reported, citing three people familiar […]
3 October 2026

N0n is a newly-emerged cyber extortion gang. The group was first spotted in the middle of September 2026, and within days it had published on its dark web leak site […]
2 October 2026
The EU is recommending import controls to combat unregulated squid fishing in the Southwest Atlantic. I’m not optimistic. As usual, you can also use this squid post to talk about […]
2 October 2026
A critical flaw in GitLab’s AI Gateway could let a logged-in user with Duo Agent Platform access run commands on the gateway under certain conditions, GitLab said in an advisory. The […]
2 October 2026
This essay was written with Nathan E. Sanders, and originally appeared in The Guardian. New campaign finance disclosure data shines a light on which US political campaigns are using AI […]
2 October 2026
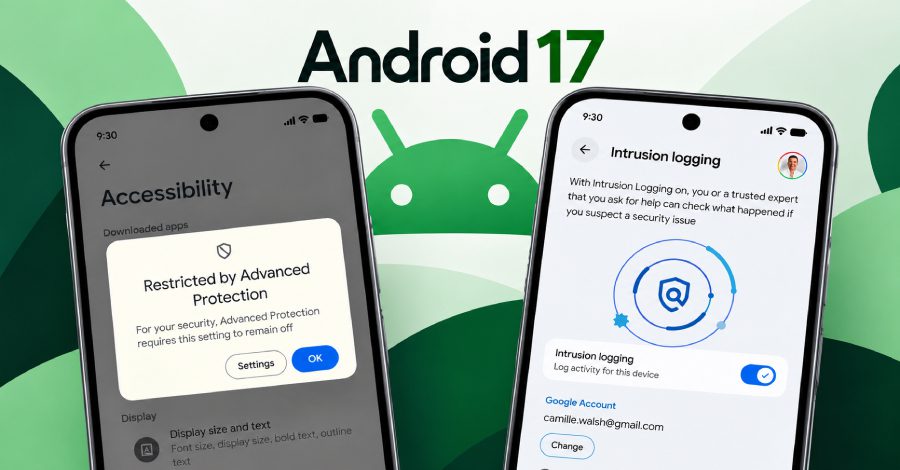
Google has announced a new security measure that limits access to Android’s accessibility services to verified applications classified as Accessibility Tools when Advanced Protection is enabled. With malicious Android applications […]
2 October 2026
ISC Stormcast For Friday, October 2nd, 2026 https://isc.sans.edu/podcastdetail/10120, (Fri, Oct 2nd)
(c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.
1 October 2026
The FBI has a very simple message for the ShinyHunters gang: give yourselves up. On Tuesday, FBI cyber division assistant director Brett Leatherman released a video, thanking the Dutch police […]
1 October 2026
Google on Wednesday announced its latest frontier artificial intelligence (AI) model, Gemini 4 Argon, that it said is being rolled out to a set of trusted cyber defenders through its […]
1 October 2026
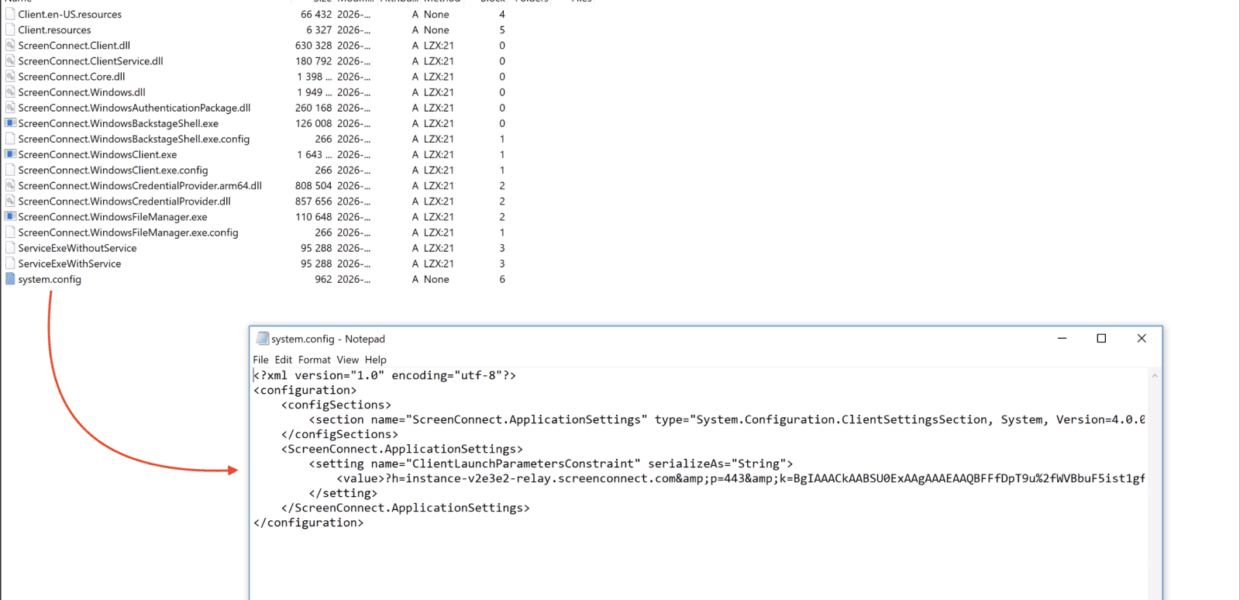
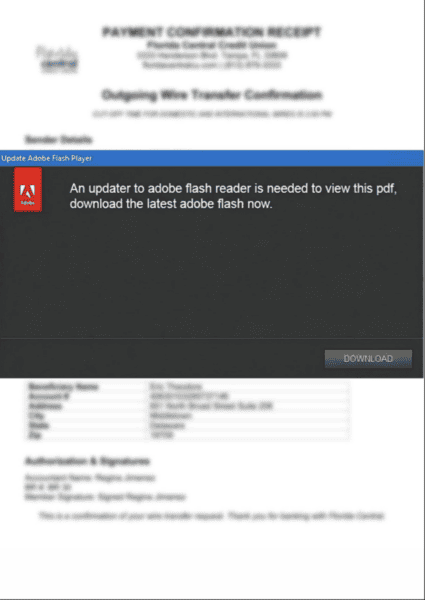


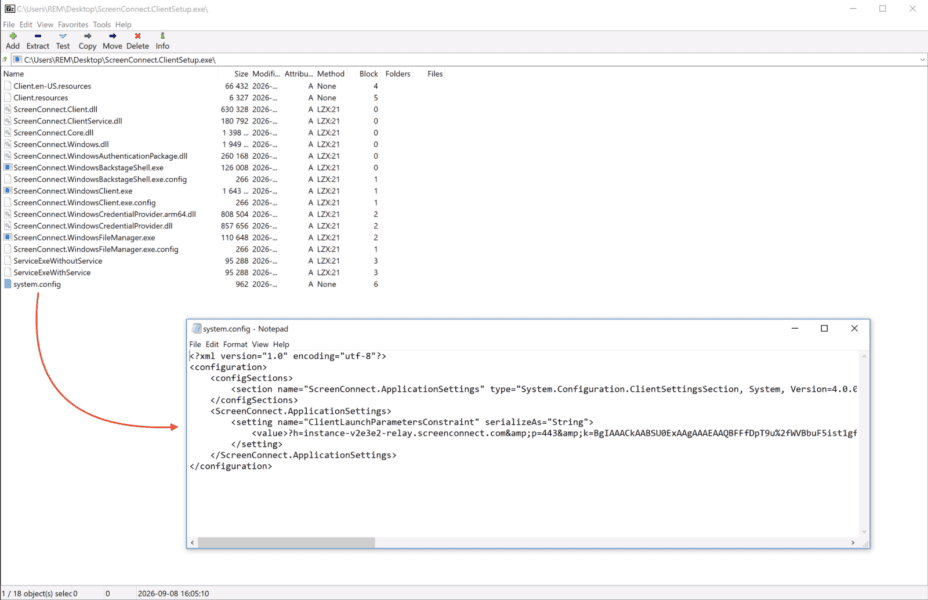
Threat Actors do not always use top-notch techniques or very complex malware to perform their attacks. Sometimes, they just abuse of existing applications… I received a very simple phishing email: […]
30 September 2026
AI systems are regularly completing tasks in ways that their prompters don’t want or intend. Some of them are disturbing, and some of them are dangerous. This is something I’ve […]
30 September 2026
A Pentagon personnel database was breached for nine months without anyone noticing. Over three million people are affected. Read more in my article on the Hot for Security blog.