


New malware that uses steganography always gets my attention, but I was disappointed when I looked at the latest DOUBLECUP write-up. It doesn’t use real steganography:
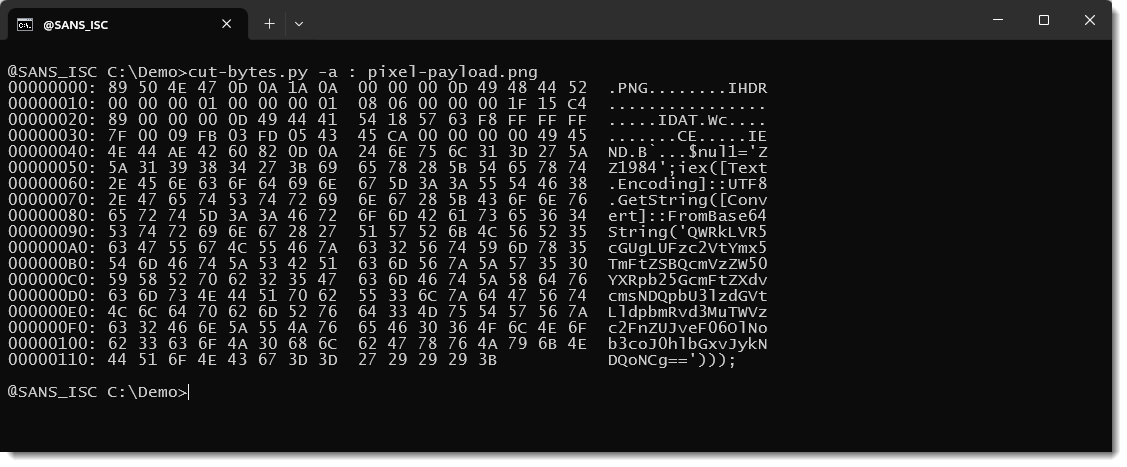
You can see the PowerShell payload as cleartext: it has not been encoded into the pixels of the image.
It’s even not embedded in the image (like inside the metadata), it’s just appended after the PNG file:
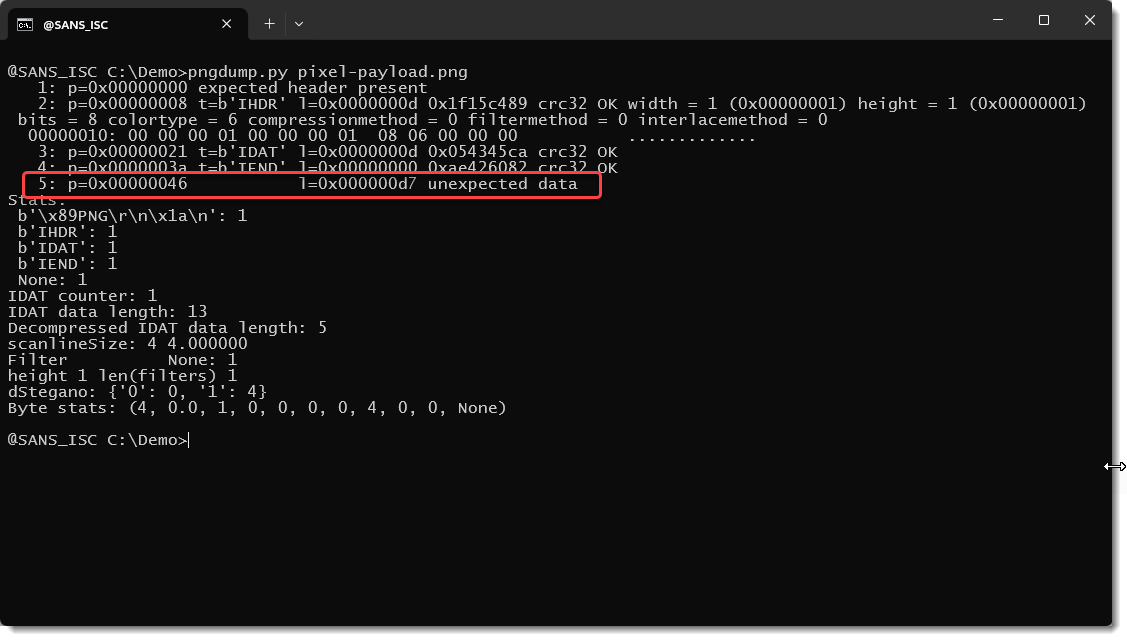
Yet there is a clever little trick:
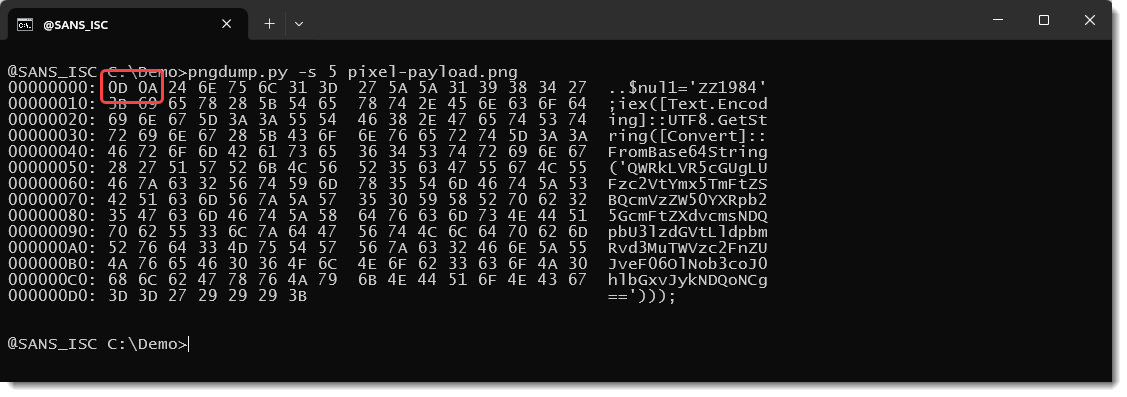
The PowerShell script starts with 0x0D 0x0A, Carriage-Return + Newline: that terminates a line of text in Windows.
That makes that you don’t need a custom payload extractor, you can just use the FINDSTR command (Windows’ grep) with a unique identifier to extract the script:
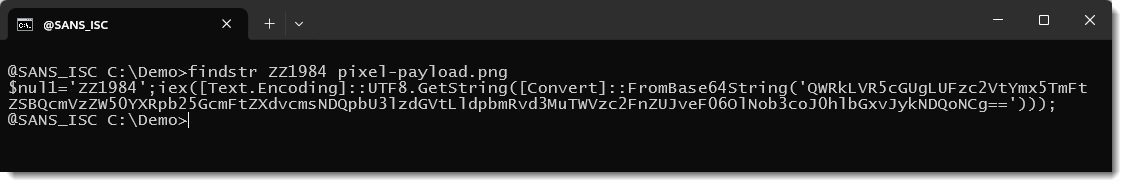
And then pipe it into the PowerShell interpreter.
Didier Stevens
Senior handler
blog.DidierStevens.com
(c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.

